![OmniByte - PNG Black Logo Oct 2021 (1).png]](https://help.omnibyte.com/hs-fs/hubfs/OmniByte%20-%20PNG%20Black%20Logo%20Oct%202021%20(1).png?height=50&name=OmniByte%20-%20PNG%20Black%20Logo%20Oct%202021%20(1).png)
The Sync Users window retrieves the necessary information from Azure Active Directory (Azure AD) to identify users when using Single Sign-On (SSO). This allows users to start using forms as quickly as possible. To enable syncing, a connection or integration must be established with Azure AD, and the users must already be part of the designated Azure AD group.
Important: Administrator permissions are applied at the group level during synchronization. The Administrator setting is all or nothing for the selected group. If a group contains both administrators and non-administrators, you cannot use the Administrator checkbox to assign administrator permissions to only some members of that group.
We recommend creating two separate Azure AD groups:
- Administrator group — contains only users who should have administrator permissions.
- Non-administrator group — contains users who should not have administrator permissions.
The two groups can be assigned the same application role if required. They must still be managed and synchronized separately because the Administrator setting applies to every user in the selected group.
For example:
| Azure AD group | Users | Role | Administrator |
|---|---|---|---|
Forms-Users |
Non-administrator users | Forms User | No |
Forms-Administrators |
Administrator users | Forms User | Yes |
This configuration prevents regular users from receiving administrator permissions while allowing designated administrators to retain their administrator access.
Important: Do not place administrators and non-administrators in the same group if you need to synchronize them using different administrator settings.
- From the Administration menu, click Users to open the Users page. In the upper right, click Sync Users. The Sync Users window opens.
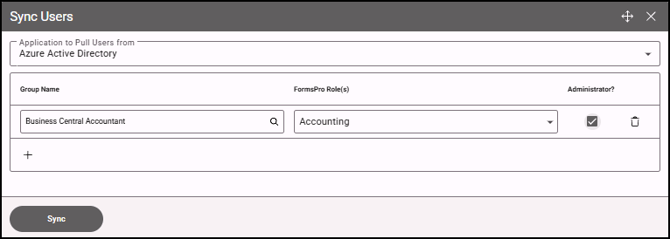
- From the Application to Pull Users from field, select Azure Active Directory.
- Click
 to specify the users to sync.
- Select the group name and roles.
- Specify whether the selected group has administrator rights:
- Administrator selected: All users in the selected Azure AD group are synchronized as administrators.
- Administrator not selected: Users in the selected group are synchronized as non-administrators. If users who currently have administrator permissions are synchronized from this group without the Administrator option selected, their administrator permissions will be removed.
- Click Sync to synchronize the user information.
This group structure provides a predictable way to manage administrator permissions through Azure AD while allowing users to be synchronized automatically for SSO.